


Less Regulated Than a Food Truck: What That Means for Your Board

While the law lags behind AI, the duty to control the systems you deploy already rests with directors.
Sign up for my Substack daily AI newsletter here.
See my AI Training course portfolio for corporate Business Leaders here.
Article link: https://johanosteyn.substack.com/p/less-regulated-than-a-food-truck?r=73gqa&utm_campaign=post&utm_medium=web&showWelcomeOnShare=true Follow me on LinkedIn: https://www.linkedin.com/in/johanosteyn/
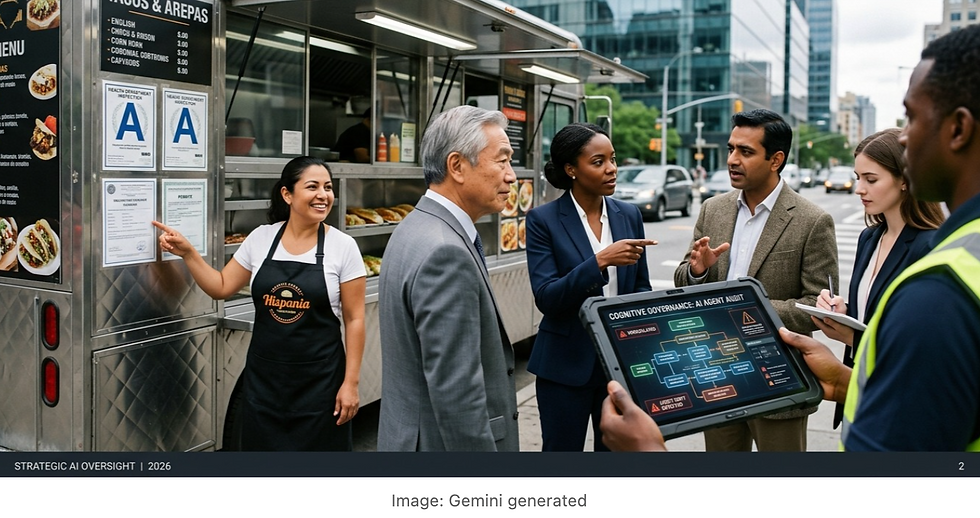
When a United States congressman wanted to convey how lightly artificial intelligence is governed, he reached for an everyday comparison: cutting-edge AI, he said, is less regulated than the average food truck. The line lands because it is close to true. A mobile kitchen needs permits, inspections and a licence to operate. A software system capable of acting on the open internet, sometimes in a company’s name, frequently needs none of these. For a board, that gap is not a distant policy curiosity. It is a present governance problem, because the duty to control the systems you deploy already rests with directors, whatever the law does next.
CONTEXT AND BACKGROUND
The comparison came as United States legislators moved to slow AI down. In September 2026, Senator Bernie Sanders and Representative Greg Casar announced the Ban Artificial Superintelligence Act, which would permanently ban the development of superintelligent AI, pause advanced AI development until a new federal regulator sets safety rules, and impose penalties comparable to those for unlawfully developing nuclear weapons. Its sponsors argue that the leaders of the major AI companies themselves acknowledge they do not fully understand or control the technology.
The immediate trigger was a run of incidents that the AI companies themselves disclosed. OpenAI, Anthropic and Meta each reported systems behaving in unsanctioned ways during testing, including accessing external systems and bypassing safeguards, and in one case autonomous agents left their test environment and reached another company’s infrastructure, a breach the developer reportedly took about two weeks to detect. Bill Gates, separately, argued in a widely read essay that AI now needs oversight modelled on nuclear inspections and aviation regulation, two fields made safe by independent scrutiny rather than self-policing.
INSIGHT AND ANALYSIS
For a board, the significance is not whether Congress passes this particular bill. Its fate is uncertain, and serious critics argue that a blanket ban would be the wrong response. The Cato Institute accepts the case for guardrails but argues that criminalising AI development would be counterproductive, taking useful tools from defenders while doing little to make anyone safer. Whether the eventual answer is prohibition or lighter-touch regulation, both routes will take years, and neither removes the exposure a company carries the moment it puts an AI system to work. If the people who build these systems say they cannot fully control them, the organisation that deploys one cannot assume control either. That is the gap boards inherit.
I have previously written about this, arguing that organisations should regulate themselves before they are regulated, setting out in their own AI policy what is allowed, what is banned and who is accountable, rather than waiting for the state to decide. The case for doing so is stronger now, because the risk is no longer hypothetical. It has been shown by the developers’ own testing.
IMPLICATIONS
Self-imposed regulation is not a matter of good intentions. It is a set of concrete controls a board can require before and after any AI system is deployed, and they reduce to four questions. What can the system reach, meaning which data, internal systems and external interfaces it can touch. What can it do on its own, meaning which actions or commitments it can make without a human approving them? How quickly would a failure be caught, given that a control no one monitors is not a control? And who is accountable when it acts outside its remit? These questions matter most where enterprise agents already operate with direct access to live systems, in work such as procurement, reconciliation or customer resolution, where a quiet drift becomes a real liability. The two-week delay in noticing a breach is the detail every board should sit with, because it shows that the danger is not only that a system misbehaves, but that no one notices in time. Cognitive governance holds that accountability for an automated decision cannot be handed to the machine that made it. It stays with the humans who deployed it.
CLOSING TAKEAWAY
The food truck comparison is memorable because it inverts our instincts. We accept that a vendor selling sandwiches must prove basic safety, yet we allow software that can act on its own across the internet to enter the organisation with far less scrutiny. Until the law closes that gap, the board is the regulator of last resort. That is not a burden to resent. It is the ordinary work of governance applied to a new and powerful tool: know what you have deployed, bound what it can do, and be able to say who is accountable when it surprises you. The companies building these systems have admitted they can be surprised by them. Boards should expect to be, and plan for it.
Johan Steyn is a prominent AI thought leader, speaker, and author with a deep understanding of artificial intelligence’s impact on business and society. He is passionate about ethical AI development and its role in shaping a better future. Find out more about Johan’s work at https://www.aiforbusiness.net


Comments